
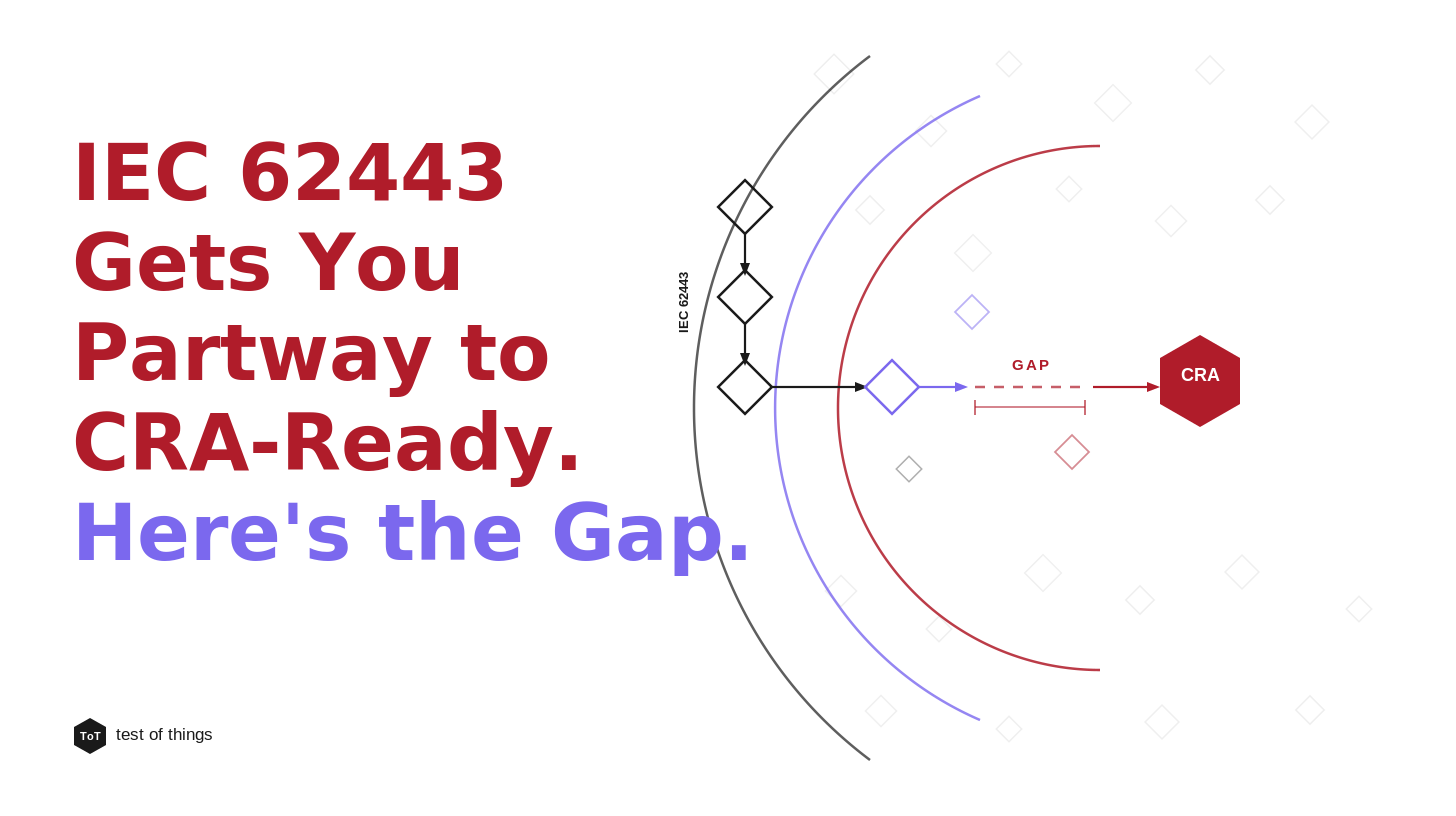
IEC 62443 Gets You Partway to CRA-Ready. Here's the Gap
IEC 62443 is a strong foundation — but it doesn't fully satisfy the EU Cyber Resilience Act. Here's exactly where the gap is and what manufacturers need to close it.

Access Control Under the CRA: More Than Just a Login Screen
Part #6 of our Human Written CRA series unpacks Annex I Part I requirement 2(d): from MFA and machine-to-machine TLS to unauthorized access reporting, surface reduction, and substantial modification triggers.

EU’s Official CRA Guidance: What Connected Product Makers Need to Know
The European Commission has officially released its guidance to support the implementation of the Cyber Resilience Act (CRA).
Here is a breakdown of the key takeaways from the Commission’s release and what it means for your automated compliance strategy.
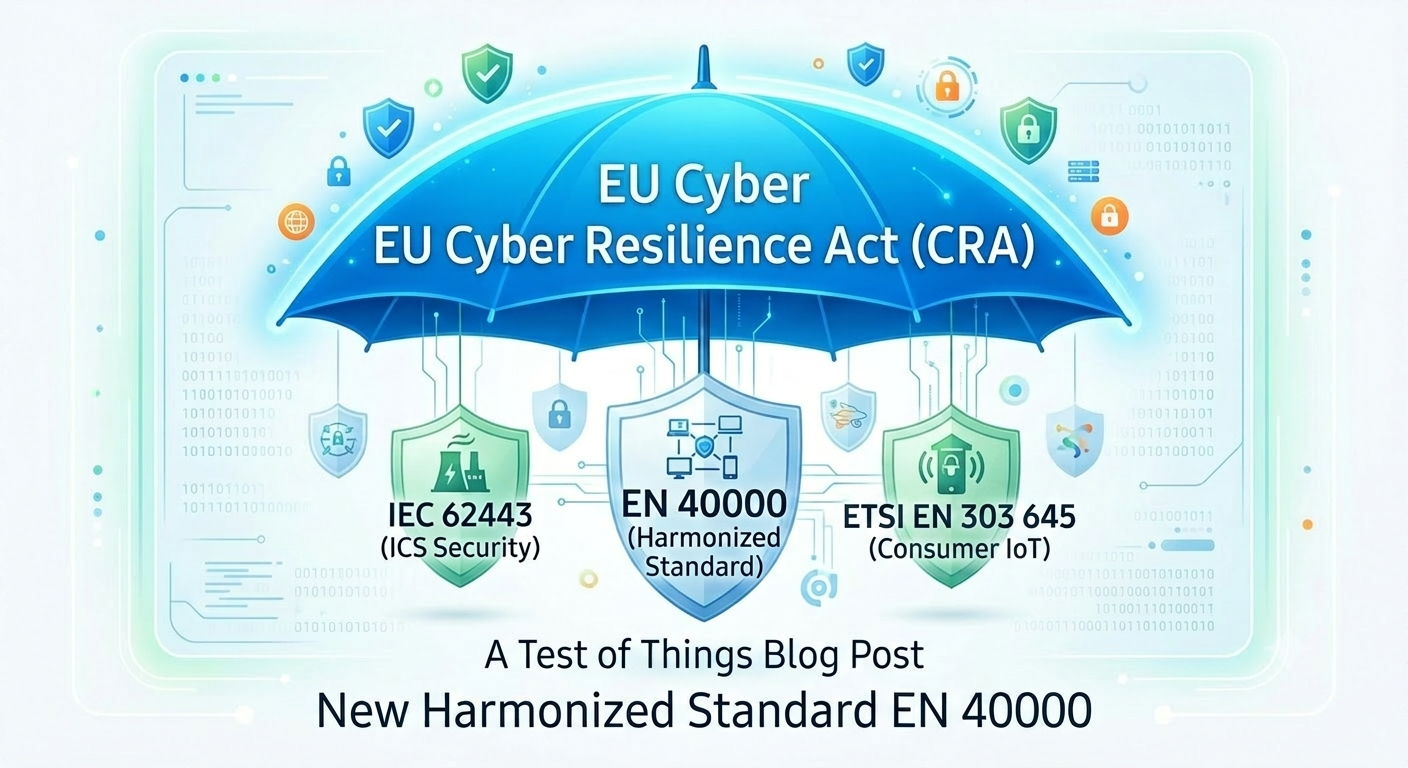
EN 40000 Explained: The Technical Blueprint Behind the EU Cyber Resilience Act
The CRA sets the legal rules for product cybersecurity — EN 40000 is the technical blueprint for meeting them. Here's how the four-part standard works and why it matters for your compliance strategy.

Test of Things development is co-funded by EU
The European Union has taken decisive action to address cybersecurity issues by introducing new regulations like the Radio Equipment Directive (RED) and the Cyber Resilience Act (CRA). We are proud to be supported by the European Union in developing our innovative technology further.
The goal is to develop a product prototype that is easy to use and allows users to self-assess their product’s compliance with the security standards and regulations. The grant empowers us to further our mission of protecting customers and society from cyber incidents by making IoT cybersecurity testing easy and automated.

EU Cyber Resilience Act (CRA): Vulnerability handling requirements
Tackling vulnerabilities is at the top of the CRA’s priority list. Device manufacturers and developers will need to offer customers support for the expected product lifetime or five years, whichever is shorter. During that period manufacturers are obliged to address and correct security flaws promptly.

EU Cyber Resilience Act (CRA): Essential Cybersecurity Requirements
In this post, we focus on EU Cyber Resilience Act’s essential security requirements.
Cyber Resilience Act obligations for IoT manufacturers, importers, and distributors
Cyber Resilience Act obligations for IoT manufacturers, importers, and distributors