
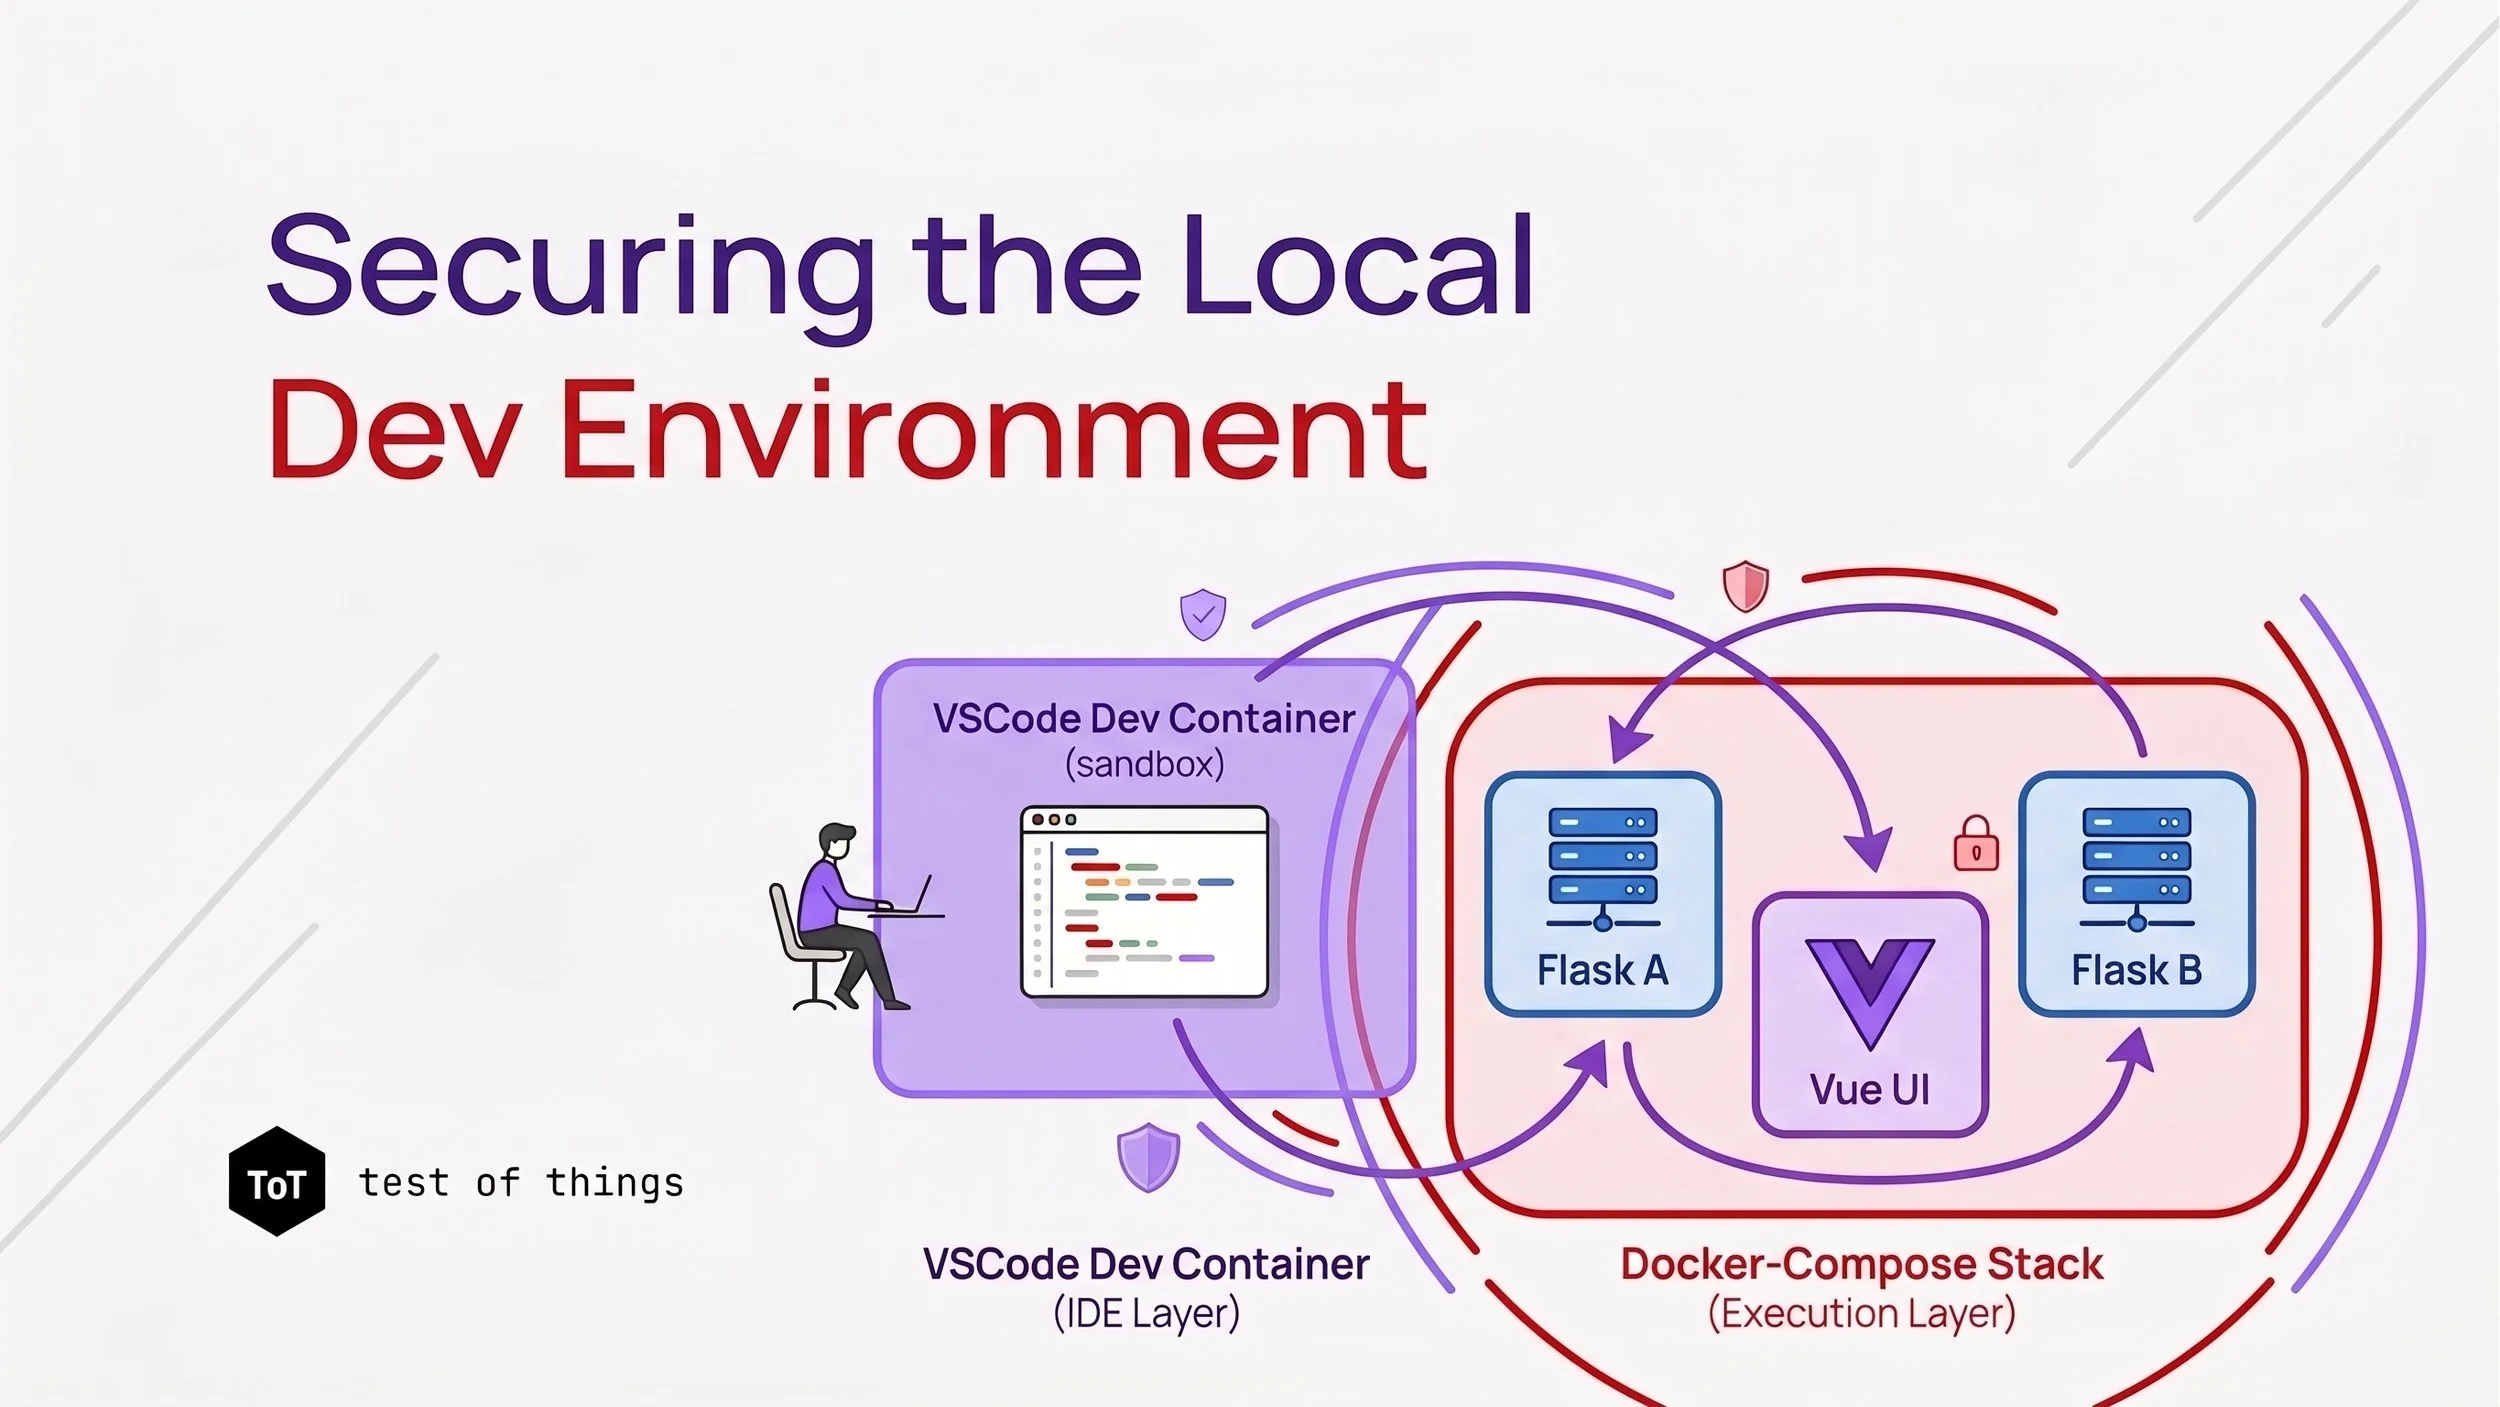
Setting Up a VSCode Dev Container for a Multi-Service Architecture
Supply chain attacks targeting package registries like npm and PyPI make local developer isolation critical. Learn how our senior engineer sets up a secure, single-window VSCode Dev Container environment for a multi-service architecture.
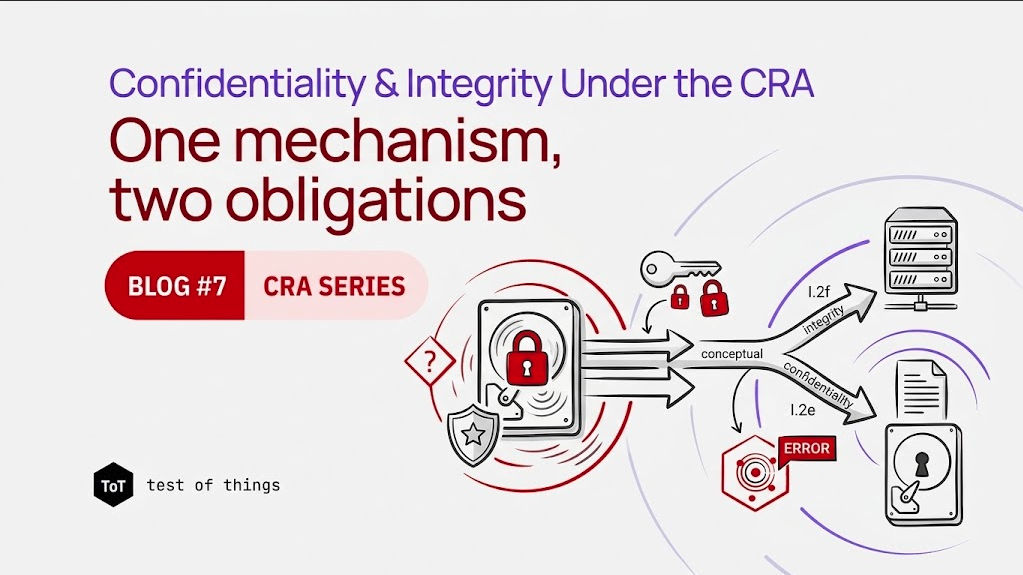
Confidentiality and Integrity Under the CRA: One Mechanism, Two Obligations
CRA Annex I requirements 2(e) and 2(f) both protect data — but confidentiality and integrity are separate obligations that just happen to share a mechanism like TLS. Here's why treating them as one and the same is how compliance gaps get missed.
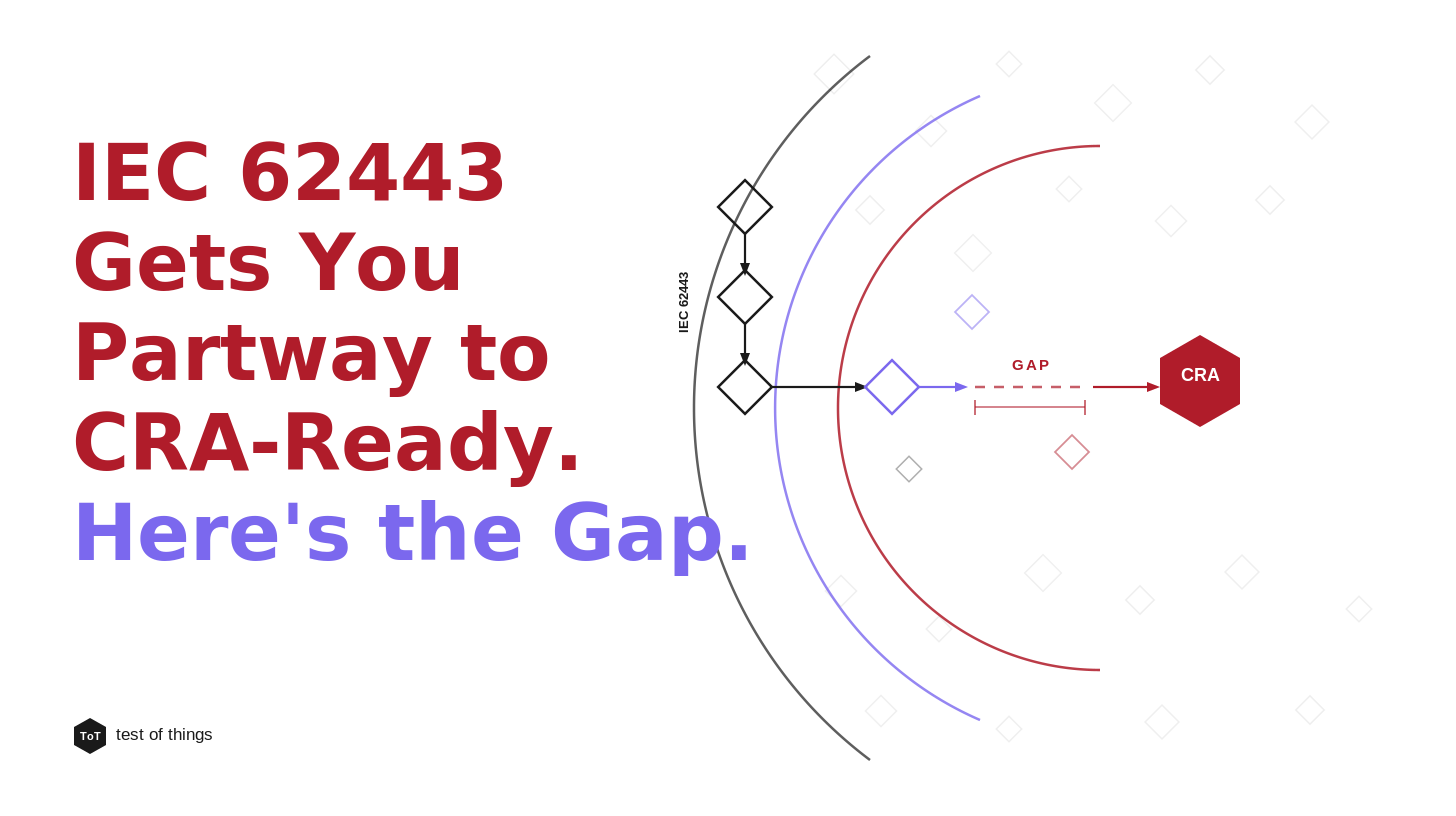
IEC 62443 Gets You Partway to CRA-Ready. Here's the Gap
IEC 62443 is a strong foundation — but it doesn't fully satisfy the EU Cyber Resilience Act. Here's exactly where the gap is and what manufacturers need to close it.
Access Control Under the CRA: More Than Just a Login Screen
Part #6 of our Human Written CRA series unpacks Annex I Part I requirement 2(d): from MFA and machine-to-machine TLS to unauthorized access reporting, surface reduction, and substantial modification triggers.
EU’s Official CRA Guidance: What Connected Product Makers Need to Know
The European Commission has officially released its guidance to support the implementation of the Cyber Resilience Act (CRA).
Here is a breakdown of the key takeaways from the Commission’s release and what it means for your automated compliance strategy.
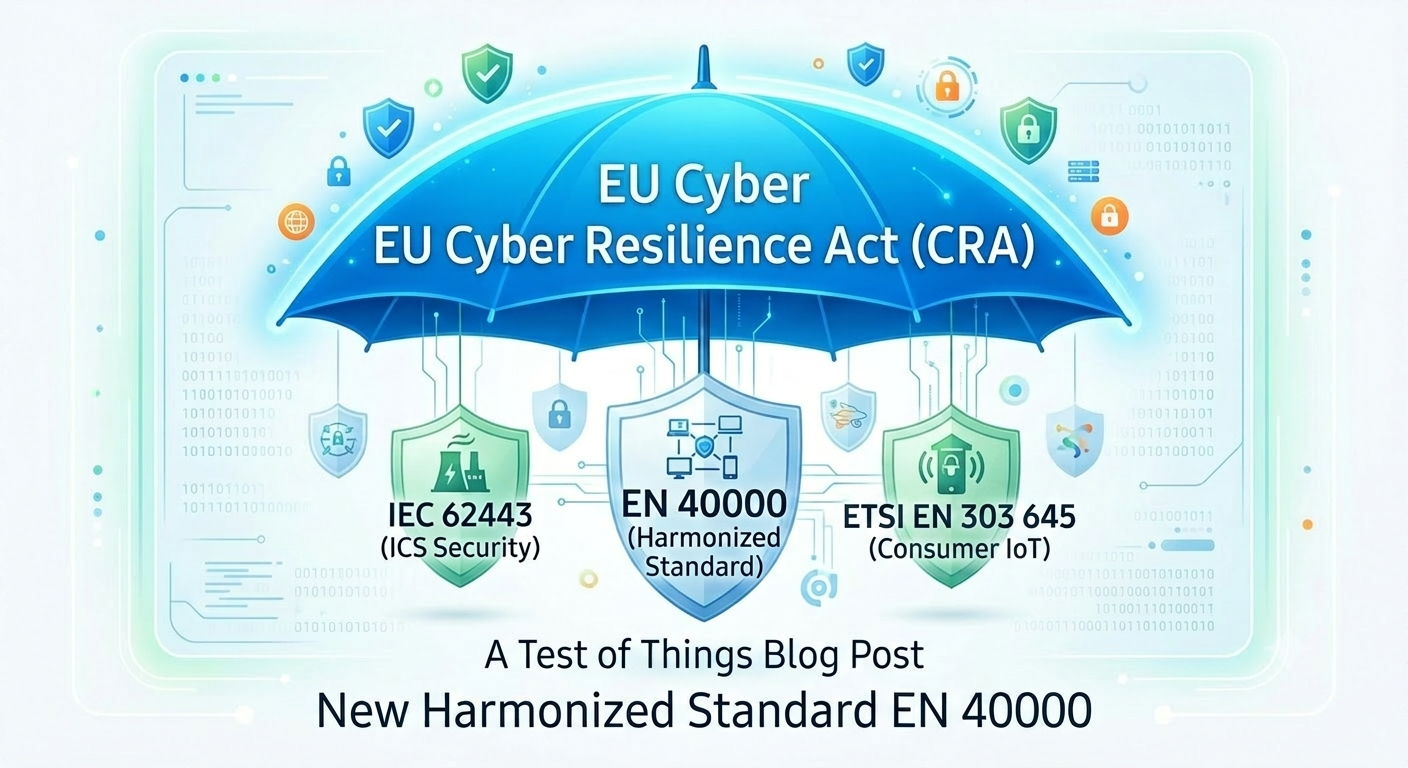
EN 40000 Explained: The Technical Blueprint Behind the EU Cyber Resilience Act
The CRA sets the legal rules for product cybersecurity — EN 40000 is the technical blueprint for meeting them. Here's how the four-part standard works and why it matters for your compliance strategy.
Secure by default: CRA's baseline security expectations
Blog #5 in our Human Written CRA expert series: The EU Cyber Resilience Act flips security responsibility onto manufacturers. Learn what “secure by default” really demands for configurations, updates, features, and data collection.

Software Bill Of Materials (SBOM)
Blog #4 in our Human Written CRA expert series: What's actually running in your product? Most teams don't know. Learn how to generate an SBOM — from source code to binaries — and why the CRA requires it.
No Known Exploitable Vulnerabilities
Blog #3 in our Human Written CRA expert series: What “no known exploitable vulnerabilities” actually means under the CRA—and how SBOMs, risk assessment, and automation help you meet the new security and reporting duties.
CRA risk assessment
Blog #2 in our Human Written CRA expert series: Turn CRA’s abstract risk assessment requirement into a concrete, 3‑step process: define scope, identify assets, and prioritize risks by likelihood and impact to guide secure product design.

Does CRA apply to your product? Product functions, boundaries, and components.
Blog #1 in our Human Written CRA expert series: Learn how to tell if CRA applies to your product by clarifying intended purpose, core and essential functions, and mapping product boundaries, components, and external dependencies.
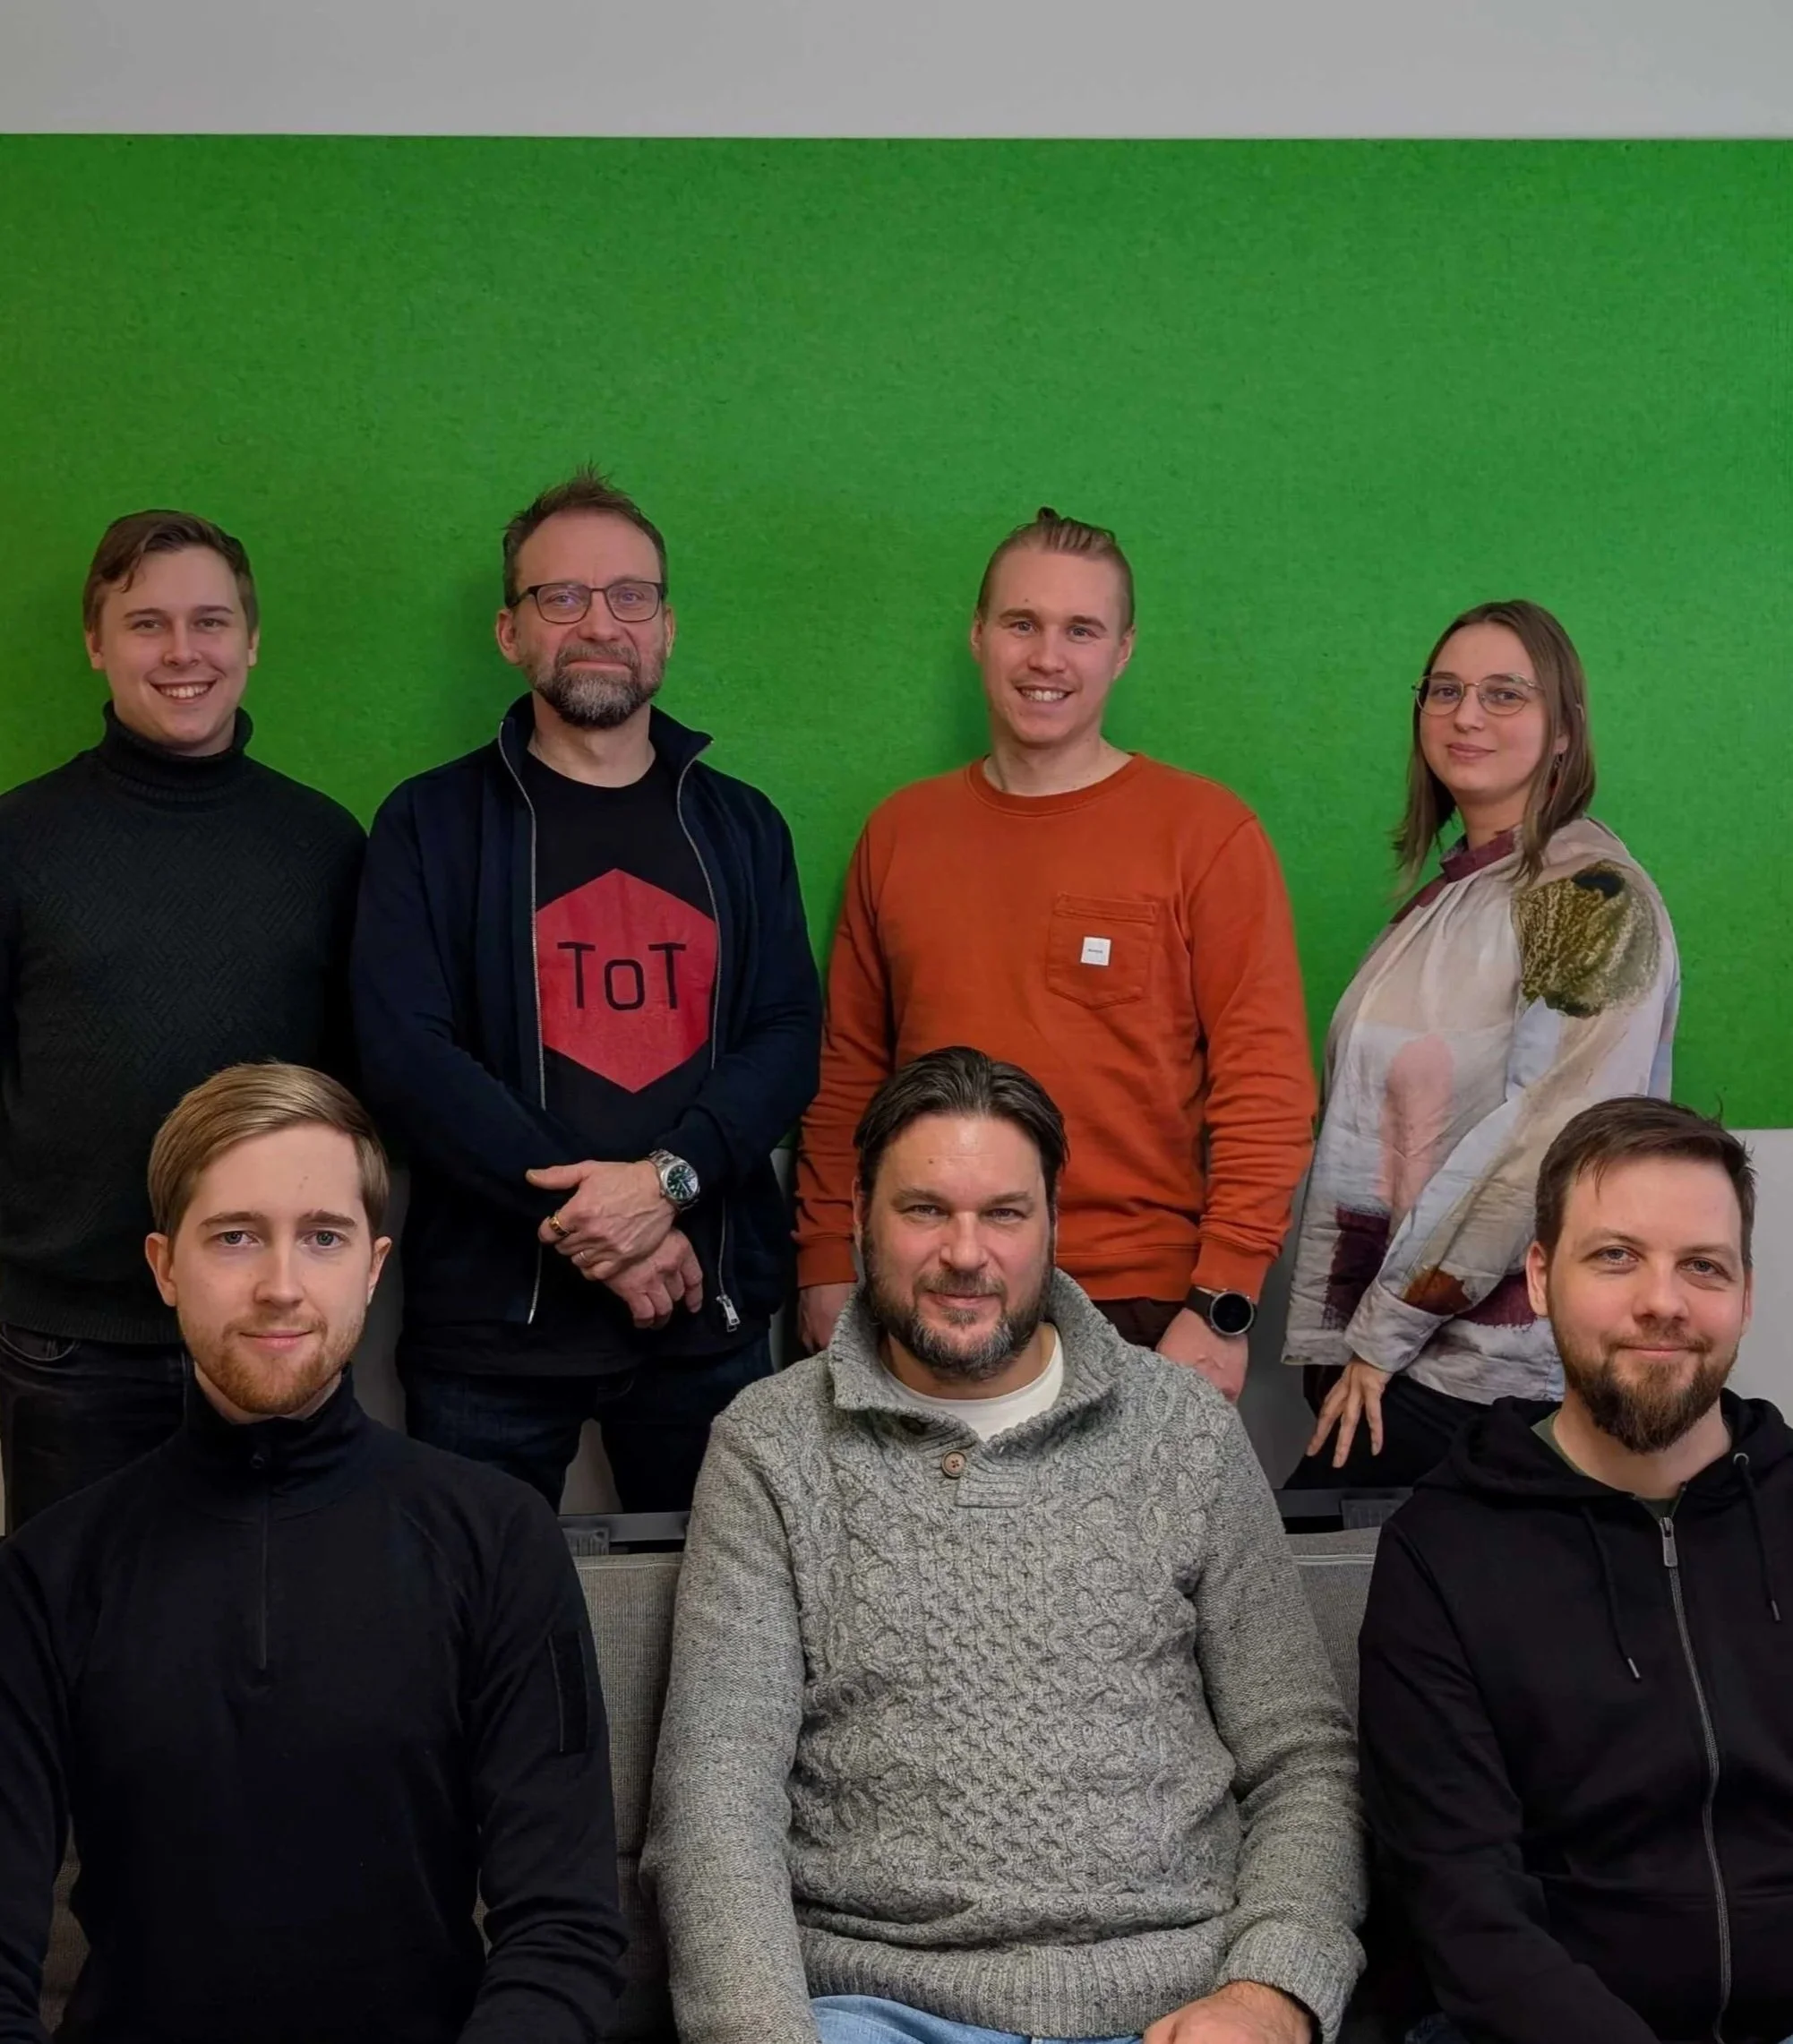
Test of Things raised €1.2 million to fix the cybersecurity problem of connected devices
Test of Things, a cybersecurity startup, has just raised a €1.2 million pre-seed funding round to help connected product manufacturers to automate cybersecurity testing and compliance management.
Research: Navigating the Overlaps and Gaps in 16 IoT cybersecurity requirements
A research-backed look at 16 IoT cybersecurity requirements—where they align, where they clash, and how to build one practical, testable baseline for secure, compliant connected products.

Research data: Top vulnerabilities in the IoT systems
New research shows most IoT vulnerabilities are not in the device, but in cloud backends, web frontends, and mobile apps—revealing why HTTP and injection flaws drive real-world IoT attacks.

The EU CRA Countdown: Why September 2026 is Your Real Deadline
September 2026 triggers 24‑hour vulnerability reporting under the EU CRA. See why that date, not 2027, is your real deadline—and how to get ready in time.
The Benefits of Using Cybersecurity Compliance Management Tools for IoT manufacturers
IoT compliance has evolved from a checkbox to a strategic imperative. Learn how specialized compliance management tools transform regulatory burden into competitive advantage for IoT manufacturers.

Quantifying Cyber Risk: A CFO’s Guide to Investing in IoT Product Security
Discover how to translate IoT vulnerabilities into concrete financial risk, avoid costly recalls and fines, and turn product security into a high-ROI, board-level investment decision

The CRA and Your Backend: When the Cloud Platform Becomes Part of the Product
The EU Cyber Resilience Act doesn't just regulate IoT hardware—it includes your backend too. Learn when cloud platforms become part of your product and what compliance requirements you must meet.
Test of Things is end-to-end connected system cybersecurity compliance and testing platform covering devices, back-ends and for example mobile applications.
Stay compliant continuously and ship with confidence.
IEC 62443-4-1: Your Strategic Gateway to EU CRA Compliance
IEC 62443-4-1 provides a proven framework for IIoT and OT manufacturers to meet most EU CRA requirements. Learn how this secure development lifecycle standard accelerates your CRA compliance journey.
Vulnerability Management under the CRA: What the New Reporting Rules Mean for You
The EU CRA introduces strict 24/72-hour vulnerability reporting for manufacturers, demanding rapid response, proactive testing, and transparent communication—or risk heavy fines and lost trust.