
Meet us at Cybersecurity & Cloud Expo in Amsterdam on October 19-20
-
Meet us at Cybersecurity & Cloud Expo in Amsterdam on October 19-20 -
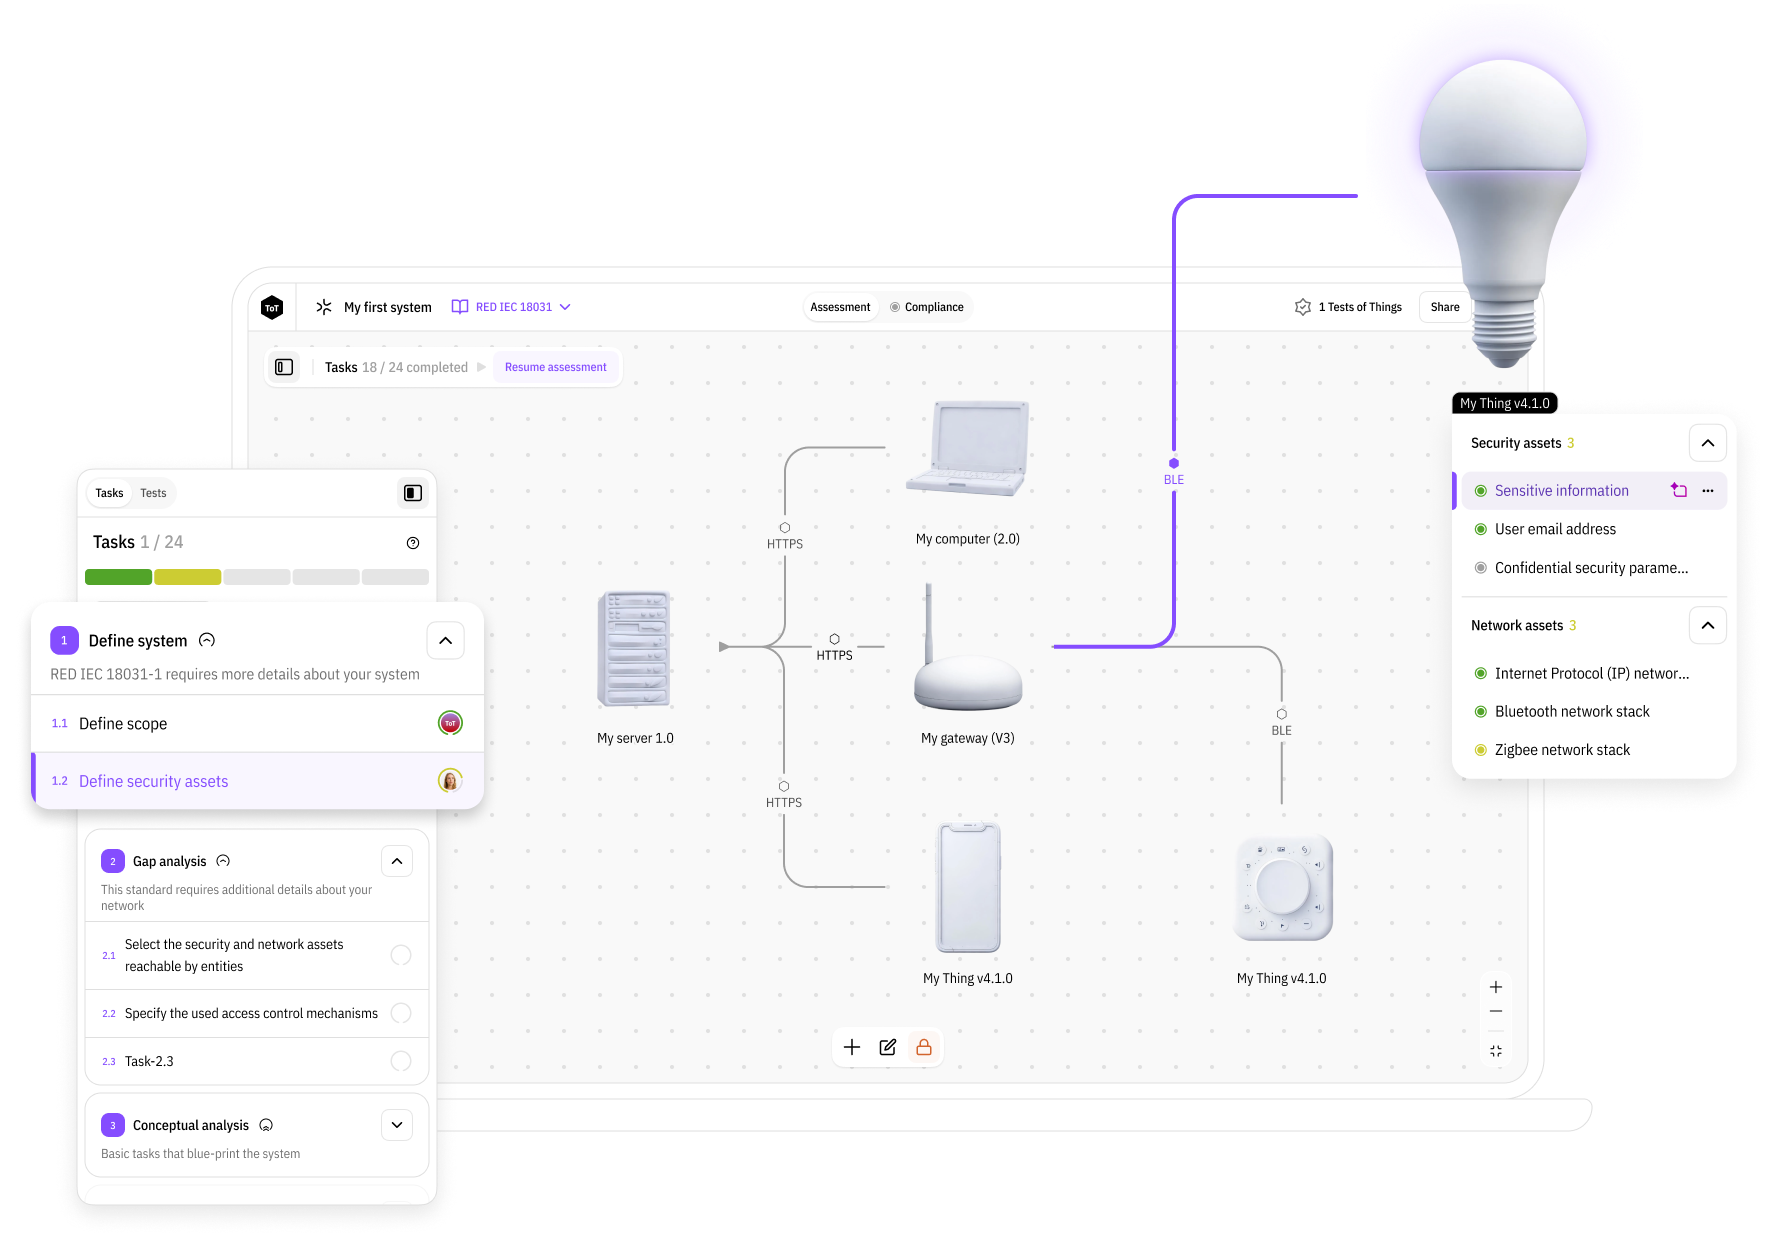
Get CRA & IEC 62443 Compliant in-house
Test of Things turns cybersecurity regulation and security standards into automated tests and developer-ready tasks — your own product teams can ship audit-ready, continuously-tested connected products. For a fraction of the cost of manual cybersecurity assessment.
So that you can ship confidently.

IoT cybersecurity compliance is misaligned
Processes are
Manual
61%
unpatched
61% of IoT devices run outdated or unpatched firmware *1

Manufacturers are
Unprepared
86% may
face fines
86% of manufacturers aren't ready for CRA. face fines up to €15M or 2.5% of revenue *3
Compliance is
Slow
41 Month
Delay
Manual testing delays launches by months — IoT time-to-market has increased 80% to 41 months *2
Complete cybersecurity compliance
management,
automation and
monitoring for IoT.
End-to-end
cybersecurity compliance,
throughout the stack.
Manage the entire compliance lifecycle on one integrated platform. An integrated workspace that unifies firmware, devices, services, documentation, and audits. Manages the entire product portfolio, all products’ compliance status in one view.
Replace multiple fragmented tools with one source of truth for your entire IoT product portfolio.
Agent
guided workflows
Test of Things AI-guided workflows are designed for product teams to achieve compliance independently.



Once compliant,
always compliant
Stay compliant 24/7, not just at certification time.Test of Things continuously monitors firmware updates, cloud changes, vulnerabilities, and SBOM shifts to detect compliance gaps in real time.

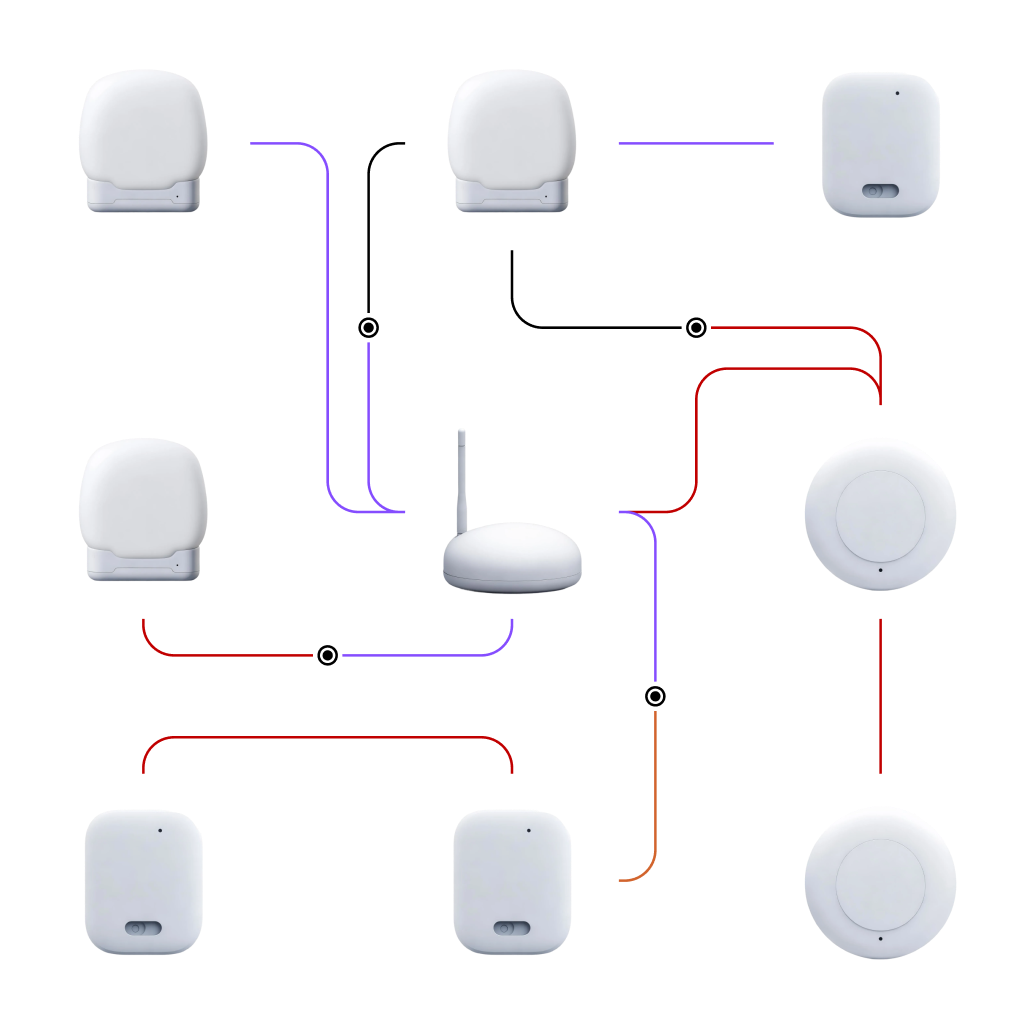
Continuous testing
Automated tool-driven testing, and scanning.
Real-time alerts
Stay updated on real-time
Evidence updates
Single source of truth for entire portfolio.
SBOM lifecycle
Automatic lifecycle integration.
Made for IoT companies,
perfected for teams.
System
Manufacturers
End-to-end
compliance management
for product companies

Industrial IoT
Suppliers
Component-level
compliance
for standalone
component makers
Keep everyone aligned
Role-based collaboration and granular user access, making it easier for security and GRC teams to delegate specific tasks to other departments, like Engineering or IT.
GRC teams
Reporting for stakeholders from all segments.

Audit support

R&D
and
Product
Off-the-shelf
support for the most critical
compliance frameworks
for industrial IoT
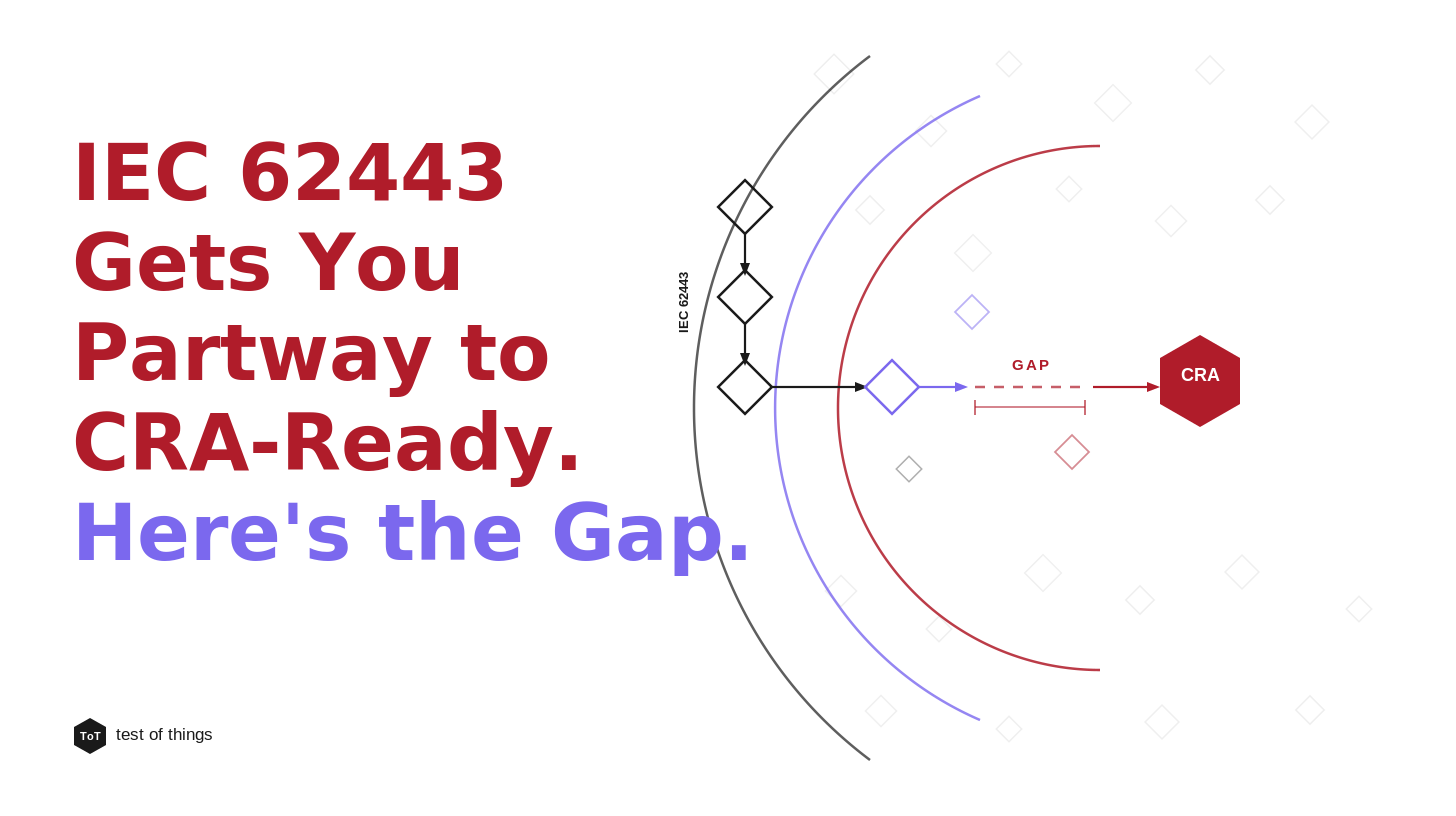
Leveraging IEC 62443-4-2 compliance towards EU CRA Compliance • Read Blog
IEC 62443-4-2
Cyber Resilience Act (CRA)
EN 40000-1-X
Build your own frameworks with Test of Things
open source tooling framework
Custom Frameworks


Did you know, the law just changed?
September 2026 saw the first CRA regulatory requirements coming for IoT industry.
Starting September 11, 2026, manufacturers of products with digital elements must report actively exploited vulnerabilities to ENISA and national CSIRTs within 24 hours of becoming aware. The EU Cyber Resilience Act (CRA) comes into full force on December 11, 2027, making every cybersecurity requirement fully enforceable and punishable across the EU market.
Stay ahead of regulatory changes with Test of Things’ real time compliance management platform.
Yesterday:
Compliance was a choice.
Test of Things helps you accelerate time-to-market and eliminate expensive consultants with compliance management platform. Get your compliance needs met for IEC 62443-3, Radio Equipment Directive (RED), Cyber Resilience Act (CRA), or any custom standard.
IEC 62443-4
Mandates an audit
De facto Industry compliance standard used across the world, originally designed for industrial devices.
Today:
Compliance is mandatory.
EN 40000-1-X series
Audit not required, but encouraged.
CRA is the law, but EN 40000 -series is the blueprint what needs to be implemented, tested and audited to be CRA compliant
Tomorrow:
Compliance has to be certified.
Cyber Resilience Act
Mandated for all connected products sold in the EU, starting 2027. Mandatory compliance that also requires an audit for critical products.
Audit required for critical devices
Stay ahead of vulnerabilities
Test of Things makes IoT device security simple. Automate your testing, run instant gap analysis, and generate compliance-ready reports — all in-house, without costly consultants.
Security standards are complex, vary by industry and region, and can slow your launch. Test of Things removes the guesswork so you can cut costs, reduce risk, and bring secure products to market faster.